Trace
Supply chain security with real time SBOMSBOM, vulnerability scanning, and licence compliance, free for five repos
Highlights
What you can do with it
- A startup keeps its dependencies compliant with local regulations.
- An enterprise clears GPL and LGPL licences before an audit.
- A development team contributes to the open rules while securing its own chain.
How to use it
- 1 Connect a GitHub or GitLab repository.
- 2 Let the system generate a real time SBOM from direct and indirect dependencies.
- 3 Run a risk scan that uses vulnerability context.
- 4 Review licences and supplier details on the dashboard.
- 5 Export the SBOM as audit evidence in CycloneDX, SPDX, or JSON.
Who it is for
Pros
- The first five repositories are free, which suits small teams.
- Classification logic is open and published as editable policy files.
- Export formats line up with what auditors expect.
Limitations
- The free tier covers five repositories, so larger estates need a paid plan.
- Scanning still needs human judgement about which risks to fix first.
- Setup requires access to your CI and repositories, so review permissions carefully.
- Vulnerability data depends on upstream feeds, and gaps there show up as gaps here.
What Trace is
Trace is a software supply chain security product from Zerberus Technologies. It was built for a specific problem: most teams cannot answer what is actually inside their software once transitive dependencies are counted. Trace generates a real time software bill of materials in CycloneDX and SPDX directly from your CI pipeline, tracking both direct and indirect dependencies. It then scans with vulnerability context instead of leaning on a plain CVE list, so it prioritises the vulnerabilities that are genuinely exploitable rather than everything with a number attached. Supplier information such as APIs, SDKs, SLA expiry, and violation history sits on a single dashboard next to your code dependencies, and licence issues like GPL and LGPL are flagged early. The first five repositories are free, and after that pricing scales by repository count.
What you can do with it
- Generate a real time SBOM in CycloneDX or SPDX from CI.
- Scan with vulnerability context so real risks surface first.
- Track suppliers, licences, and contract details in one dashboard.
- Export audit evidence in the formats auditors actually ask for.
Who it is for
- Developers who need a clear picture of what is in their builds.
- Security teams carrying supply chain risk for the organisation.
- Startups that want compliance without an enterprise sized contract.
What to watch out for
The free tier covers five repositories, so anything larger moves to a paid plan and you should model that before rollout. A scanner is not a decision maker: it will hand you a prioritised list, but someone still has to judge which fixes land first and which risks are acceptable. Setup needs access to your CI system and repositories, so review those permissions the way you would any third party integration. Vulnerability and licence data also comes from upstream feeds, and gaps or delays there appear as gaps in your report. Finally, exporting evidence satisfies a checklist, it does not by itself prove your supply chain is safe.
FAQ
Is Trace free?
The first five repositories are free, and beyond that pricing scales predictably based on the number of repositories.
What formats does it output?
It generates SBOMs in CycloneDX and SPDX, and can export audit evidence in CycloneDX, SPDX, and JSON.
Can I see how risk scores are decided?
Yes. The classification logic is public on GitHub and policies are published as forkable YAML or JSON files.
Why it is free
What the official page says: 免费
Free limits, trial length and features are decided by the official site and can change at any time.
Product preview
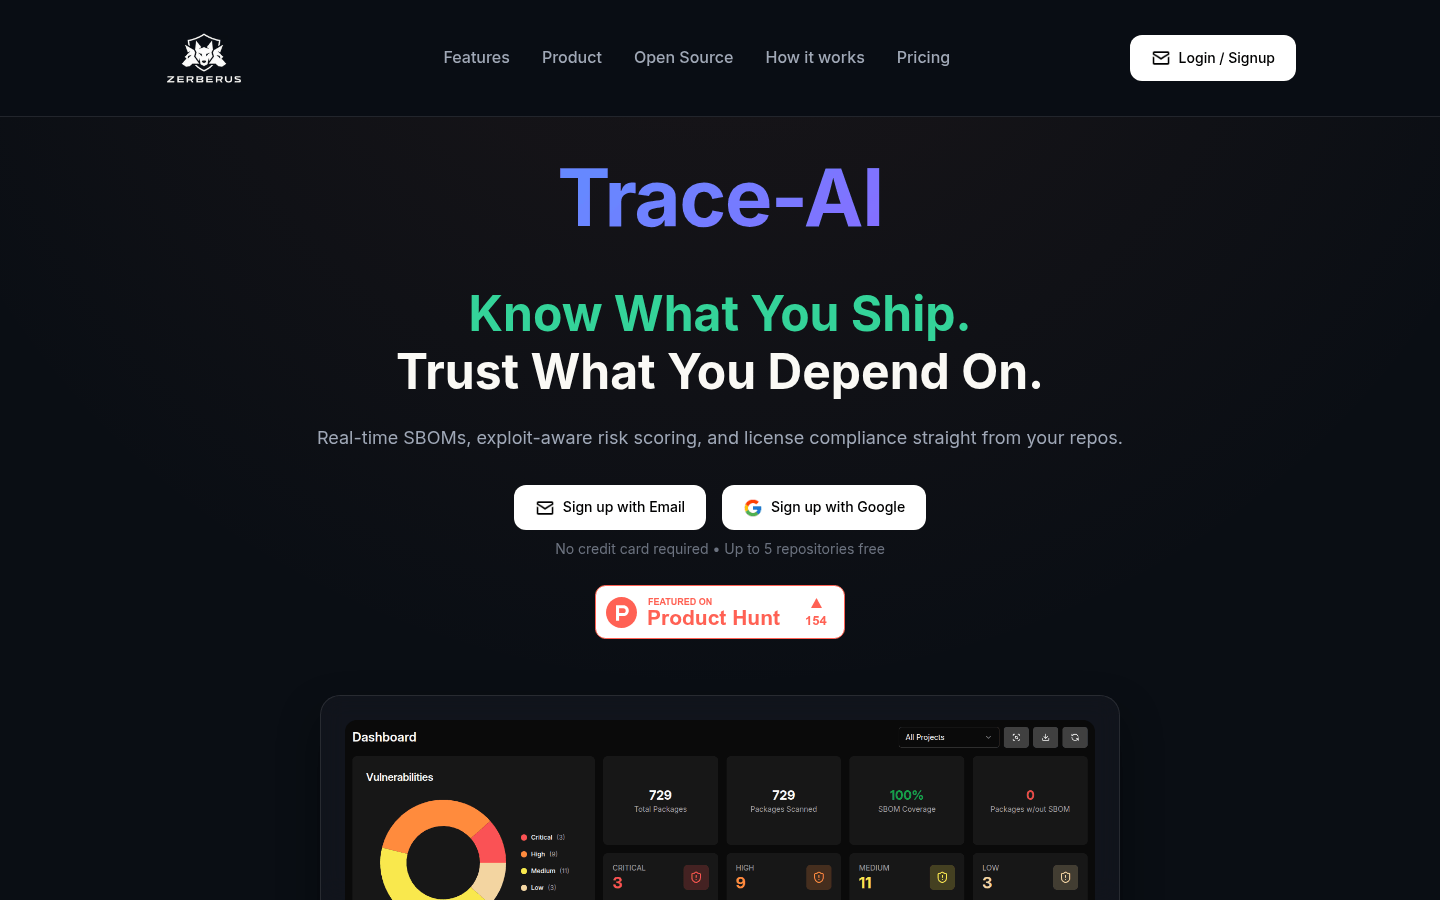
Screenshot archived from the listing page, for preview only.